
The three biggest tech concerns for a business are BYOD (employees using personal devices for work), data loss and recovery, and cybersecurity. They are linked: an unmanaged phone can leak data, and ransomware can destroy it. IBM’s Cost of a Data Breach Report 2026 puts the global average breach cost at USD 4.99 million.
Key Takeaways
- BYOD (Bring Your Own Device) means staff use personally owned phones, tablets or laptops for work; the term entered common use in 2009 through Intel, according to Wikipedia.
- CISA recommends the 3-2-1 backup rule: 3 copies of important files, on 2 different types of storage media, with 1 copy stored off-site.
- According to the Verizon 2026 Data Breach Investigations Report, 48% of all breaches involve ransomware and 31% start with software vulnerabilities.
- IBM’s 2026 report gives a global average breach cost of USD 4.99 million, a 12% increase over the previous year.
- The NIST Cybersecurity Framework 2.0 (released February 2024) gives any business a free structure: Govern, Identify, Protect, Detect, Respond, Recover.
If you run a business, then you will probably be aware of the hugely important and central role that technology plays, almost automatically, in that business. The fact is, technology and business are bedfellows, and it is often impossible to have one without the other.
Most Common Technology Problems for Businesses

If you are keen on improving your business in any way, then a focus on the tech that you use will likely make a huge difference. The truth is that technology has so many uses in business that we often forget just how diverse it can be.
Fortunately, there is plenty of advice and information about this to give you a helping hand. In this article, we are going to look at some of the major tech concerns facing any business today.
BYOD
BYOD is short for Bring Your Own Device, a policy that allows employees to use their personally owned phones, tablets and laptops for work instead of a company-issued device. According to Wikipedia, the acronym was first used in 2004 and entered common use in 2009, when Intel recognized that its employees were increasingly bringing their own smartphones, tablets and laptops to work. Supporters say BYOD lets people work on devices they already know and can reduce hardware spending; critics point to security and privacy risks, because the business has less control over a device it does not own.
BYOD can make staff easier to reach and more flexible, but an always-on culture is not automatically good for a business: it blurs work and personal time, and every personal device that holds company email or files becomes part of the attack surface. A written BYOD policy should therefore cover which devices and apps are allowed, who can see what on the device, and what happens to company data when a device is lost or an employee leaves.

Data Recovery
Businesses lose data through hardware failure, accidental deletion, theft, natural disasters and, increasingly, ransomware that encrypts files and backups. This is due to a whole number of reasons, and the truth is that there is only so much you can do to make sure that no such disaster occurs. What a business can do is prepare for the worst, with tested backups and a written recovery plan in place before any data is lost.
Recovery options have also matured, from simple off-site backups to full cloud-based recovery services. One option is disaster recovery as a service (DRaaS) from a specialist provider (Infrascale is one company that sells backup and disaster recovery services); another is an in-house IT team responsible for backups and restores. Whatever it is, modern businesses need to know what they would do if such a situation occurred – and have the resources to see it through.
Security
As we come to rely on tech more and more, the use of it becomes more and more security-conscious. Data theft is costly: IBM’s Cost of a Data Breach Report 2026 puts the global average cost of a breach at USD 4.99 million, which IBM describes as a record high. Security, therefore, is becoming a major concern for businesses around the globe, and it is easy to see why they might want to focus on this keenly.
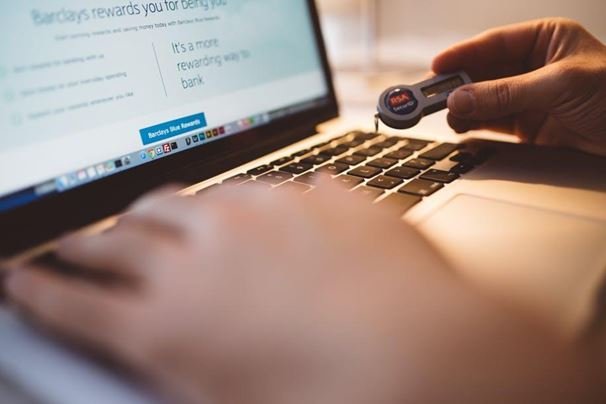
A business with a deliberate security program (backups, multifactor authentication, patching and staff training) is far better placed to keep operating after an incident, although no program removes risk entirely. These days, you can outsource this security – and it might be worth doing so, if you want to keep your business going strong.
Source
What Are the Biggest Technology Concerns for Businesses Today?
The three concerns above, BYOD, data recovery and security, remain core technology risks for most businesses, and current data shows how they overlap. The table below summarizes each concern, the main risk and the first practical step.
| Concern | Main risk | First practical step |
|---|---|---|
| BYOD | Company data on lost, unpatched or shared personal devices | Written BYOD policy plus mobile device management (MDM) |
| Data loss and recovery | Hardware failure, deletion, disasters, ransomware | 3-2-1 backups that are encrypted, partly offline and regularly tested |
| Security | Breaches through software vulnerabilities, phishing and stolen credentials | Patching, phishing-resistant MFA and staff awareness training |
How Can a Business Manage BYOD Safely?
A business manages BYOD safely by combining a clear policy with technical controls. According to Wikipedia, the main BYOD risks are data breaches from lost or unsecured devices, malware exposure, and devices whose security patching is not checked.
- Write the policy first: list approved devices and operating systems, required screen locks, and what the company may and may not see on a personal device.
- Use mobile device management (MDM): MDM lets an organization control the applications and content on a device, for example to remove company data if the device is lost.
- Consider alternatives: under COPE (corporate-owned, personally enabled), the company buys the device and allows personal use, which gives the business more control.
- Require strong sign-in: unique passwords and multifactor authentication for company apps; see this guide on how teams should manage passwords.
How Should a Business Back Up and Recover Data?
A business should follow the 3-2-1 backup rule recommended by the US Cybersecurity and Infrastructure Security Agency (CISA): 3 copies of important files, 2 different types of storage media (such as a hard drive and the cloud), and 1 copy stored off-site.
- Identify critical data: customer records, financial files, email and the systems needed to run the business.
- Apply 3-2-1: combine on-site and remote copies; this explainer on backing up and recovering data in the cloud covers the cloud side.
- Protect the backups: CISA’s #StopRansomware Guide advises keeping offline, encrypted backups of critical data, because ransomware actively seeks out reachable backups.
- Test restores: CISA advises testing that the team can restore data both fully and partially, and can roll back data at least seven days if needed.
- Choose a recovery model: disaster recovery as a service (DRaaS) from a provider, or an in-house team with documented procedures.
Which Security Threats Matter Most Right Now?
According to the Verizon 2026 Data Breach Investigations Report, which covers incidents from November 1, 2024, to October 31, 2025, 31% of breaches now start with software vulnerabilities, overtaking stolen passwords as the top way attackers get in. The same report says 48% of all breaches involve ransomware, while ransom payouts are shrinking and businesses frequently choose not to pay.
IBM’s Cost of a Data Breach Report 2026 adds that AI-driven attacks increased by 56%, led by deepfake impersonations and AI-enabled malware, and that organizations making extensive use of AI and automation in security saved USD 1.93 million compared with organizations using none. For background on the threat itself, see these common types of ransomware.
Core security steps for any business
- Patch quickly: CISA advises updating software and operating systems to the latest versions, prioritizing internet-facing servers and known exploited vulnerabilities.
- Use phishing-resistant MFA: CISA recommends it for all services, particularly email, VPNs and accounts that reach critical systems.
- Train staff: run awareness training on spotting and reporting phishing; this guide shows how to protect employees from spear phishing.
- Log and encrypt: CISA’s four cybersecurity best practices for businesses are logging, backing up data, encrypting data, and sharing cyber incident information with CISA.
- Plan for breaches: these strategies to protect a business from data breaches add practical controls.
Is There a Framework That Ties It All Together?
Yes. The NIST Cybersecurity Framework (CSF) 2.0, released by the US National Institute of Standards and Technology on February 24, 2024, organizes cybersecurity into six functions: Govern, Identify, Protect, Detect, Respond and Recover. Govern was the main addition in version 2.0 and covers the organization’s risk management strategy, expectations and policy, including supply chain risk. NIST publishes quick-start guides alongside the framework.
Frequently Asked Questions
What does BYOD stand for?
BYOD stands for Bring Your Own Device: employees use their personally owned phones, tablets or laptops for work. According to Wikipedia, the term entered common use in 2009 through Intel.
What is the 3-2-1 backup rule?
The 3-2-1 backup rule, recommended by CISA, means keeping 3 copies of important files on 2 different types of storage media, with 1 copy stored off-site.
How much does a data breach cost a business?
IBM’s Cost of a Data Breach Report 2026 puts the global average cost at USD 4.99 million, a 12% increase over the previous year. Costs for an individual business vary widely with its size and the scale of the breach.
What is the most common way attackers get into a business?
According to the Verizon 2026 Data Breach Investigations Report, 31% of breaches now start with software vulnerabilities, overtaking stolen passwords as the top entry point. Prompt patching is therefore one of the most effective defenses.
What is disaster recovery as a service (DRaaS)?
Disaster recovery as a service is a managed service in which a provider backs up a business’s systems and data and helps restore them after hardware failure, a disaster or a cyberattack, so the business can keep running.

1 Comment
Hey Harshil,
These are really amazing facts which have high impact on businesses majorly – security and Data recovery. It really hurts us when we lose some important data and unable to recover it.
This kind of issue almost everyone have to face in their whole life. But now-a-days vaious software lauched to fix this problem. Eventually, thanks for revealing a light on this topic.
With best wishes,
Amar kumar